Single sign-on with Microsoft Entra ID
There are no separate passwords to manage. Your multi-factor authentication, conditional access policies and leaver process apply to Vericia from day one.
Security
You hold the identity documents, ownership records and bank details of people who have placed their trust in you. Vericia is designed, developed and tested so that only the right people in your firm can see them, and every access is recorded.
In the product
Access is denied unless a role expressly grants it. Roles combine modules, actions and jurisdictions, so a Jersey administrator never sees a Mauritius file.
There are no separate passwords to manage. Your multi-factor authentication, conditional access policies and leaver process apply to Vericia from day one.
Read, edit and approve rights are granted by module and by jurisdiction through teams, each limited to the entities it looks after. Permissions are verified on every record, not just every screen.
Every record belongs to a single firm, identified from the signed-in account and never from the request itself. One firm's data can never be reached by another.
Tax numbers, identity documents and bank accounts show only their last four characters on screen, in registers, in exports and in Vericia AI.
KYC decisions, screening sign-offs and changes to rules or fees can each require approval by a second person.
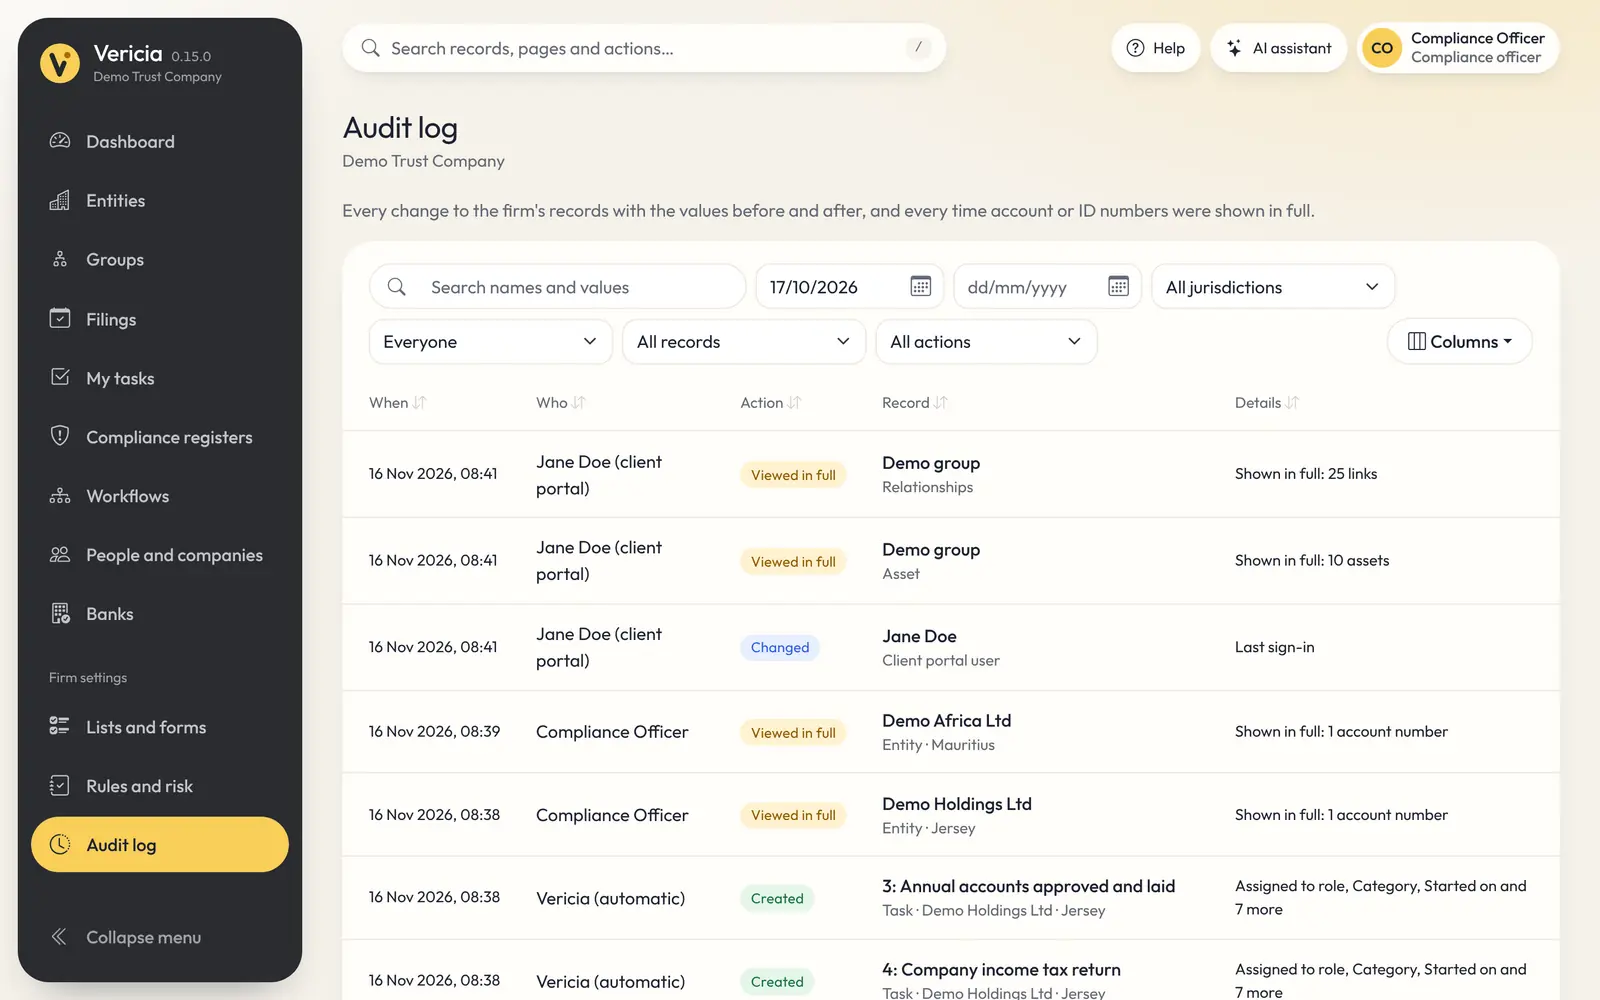
Every change is recorded with its values before and after, who made it and when, together with every occasion a masked number was viewed in full.
In how we build it
Every change follows a documented secure development policy, with automated security checks on every build. A build that fails a check is not released.
Where it runs
All connections use TLS 1.2 or later, enforced with HSTS.
Databases are encrypted with AES-256 using Azure SQL transparent data encryption.
Services authenticate to one another and to Azure Key Vault with managed identities, not stored passwords.
Automatic database backups with point-in-time restore.
A strict content security policy and security headers on every response.
If you believe you have found a vulnerability, please report it in confidence to contact@vericia.net. We will respond promptly.
AI and integrations
See it for yourself
Book a 45-minute demonstration. Tell us which jurisdictions you administer, and we will show you Vericia at work on structures like your own.